Define
Define fine-grained access policies on tables, rows, fields, data streams, anything. Or export them from existing systems.
PLATFORM
Consumer end-to-end encryption works because access is simple. Organisations have many users, far more resources, and policies that keep changing. Clave turns those policies into encryption enforced on client devices.
HOW IT WORKS
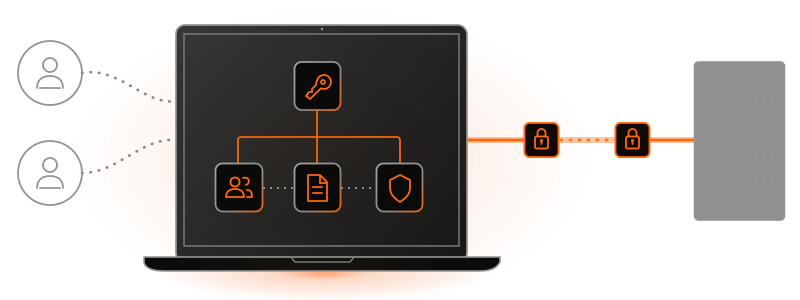
Clave's SDK sits inside the applications that create and use sensitive information. The surrounding infrastructure does exactly what it did before, only now it handles ciphertext instead of plaintext, meaning even if an attacker gets in, they can neither access nor tamper with anything.
Define fine-grained access policies on tables, rows, fields, data streams, anything. Or export them from existing systems.
Clave encrypts data to those access policies on client devices, authenticating every change to prevent tampering.
Central infrastructure handles the encrypted data without receiving decryption keys.
Authorised users and devices can access, decrypt, and modify data only when authorised by the policies involved.
THE PLATFORM
End-to-end encryption on its own is useless without key management, login, policy administration, and recovery mechanisms that are equally resilient to attacker compromise. Clave integrates those parts into one cohesive zero-trust framework, ready for adoption.
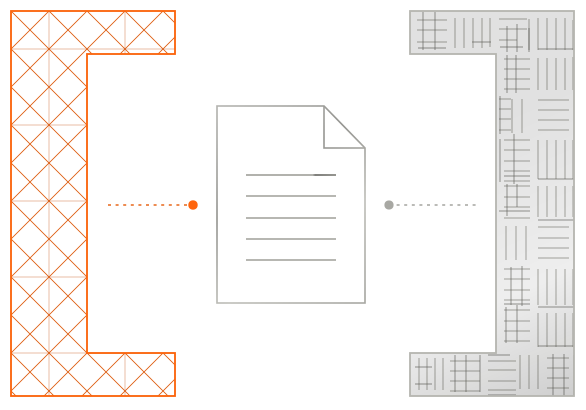
Protect or redact everything from documents to data streams under your organisation's unique access policies, however complex.
Stop server compromise from letting an attacker impersonate any user. With Clave, total compromise is accounted for.
Our software is checkpointed on distributed infrastructure, so even if an attacker hacked Clave's infrastructure and yours, they still couldn't compromise your data.
REAL-TIME PERFORMANCE
Advanced cryptography only matters if it can keep up with the system it protects. Clave secures data to complex access policies on the order of microseconds with the fastest policy-based encryption engine in the world.
HARVEST NOW? DECRYPT NEVER
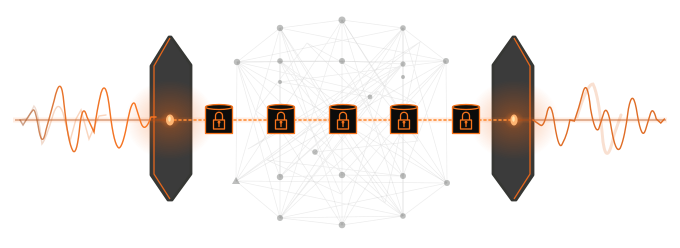
Sensitive information can outlive the cryptography protecting it today. Clave builds on algorithms standardised by NIST for the post-quantum era, with established classical cryptography as a secondary safeguard.
DEPLOYMENT
Clave can be deployed in your environment or in an untrusted cloud, integrating into existing applications and data flows rather than creating another destination for sensitive information.
Operate Clave within your own trust boundaries.
Not only can Clave run on-premise or in-cloud, but even if a cloud provider is fully compromised, your data still couldn't be compromised.
Start by protecting one important workflow, then expand as your business needs.
EVALUATE CLAVE
We'll show you how Clave can protect your most sensitive data, even against total infrastructure compromise.